MVP Permissions Checklist Before Launch
Use this MVP permissions checklist to define roles, account boundaries, sensitive actions, access tests, and safe offboarding before launch.
An MVP permissions checklist defines who can view, create, change, approve, export, or delete each important resource before launch. Start with account boundaries, a small role model, server-side authorization, sensitive actions, invitations, support access, audit history, and offboarding. The first version does not need enterprise-grade access control, but it does need rules that are explicit, testable, and enforced beyond the interface.
Permissions should follow the product’s core workflow. If the MVP lets teams collaborate, manage private records, approve work, or control billing, unclear access can make the product test unsafe or misleading. Add permission checks to the broader MVP launch checklist rather than treating them as a later settings feature.
What permissions does an MVP actually need?
An MVP needs the smallest permission model that protects its real account boundaries and launch-critical actions. That may be one authenticated user type, two workspace roles, or a separate internal support role. It should not include hypothetical departments, elaborate policy builders, or dozens of toggles unless the product test genuinely depends on them.
Separate three concepts before designing screens:
- Authentication confirms which account is making a request.
- Authorization decides whether that account may perform the requested action on the requested resource.
- Entitlements decide which features or limits are available under a plan, purchase, or configuration.
These concepts may meet in one interface, but they answer different questions. A paid feature is not automatically an administrator permission. A signed-in user is not automatically authorized to open every record with a guessable URL.
Use the scope discipline in how to scope an MVP without overbuilding: cover the roles and actions required for the core product test, then document later access needs without implementing them prematurely.
Map permissions from resources and actions
Do not begin with role names such as “manager” or “editor.” Begin with the product’s resources and the actions available on each one.
List the launch-critical resources, for example:
- Workspace or organization
- User profile
- Project, request, or case
- Generated result or document
- Invitation
- Integration connection
- Billing record
- Configuration or feature flag
For each resource, list actions such as view, create, edit, submit, approve, archive, delete, export, invite, or transfer. Then identify which actor needs each action and under what conditions.
A compact permission matrix exposes ambiguity:
| Resource and action | Owner | Member | Internal support |
|---|---|---|---|
| View workspace records | Yes | Assigned scope | Only through approved support access |
| Invite a member | Yes | No | No |
| Edit own draft | Yes | Yes | No |
| Approve a submitted item | Yes | If assigned | No |
| Change billing owner | Yes, with confirmation | No | No |
| Diagnose a failed job | Summary only | Summary only | Approved diagnostic view |
Replace every vague cell with a testable rule. “Limited access” is not a rule until the team can explain the exact records, fields, and actions it permits.
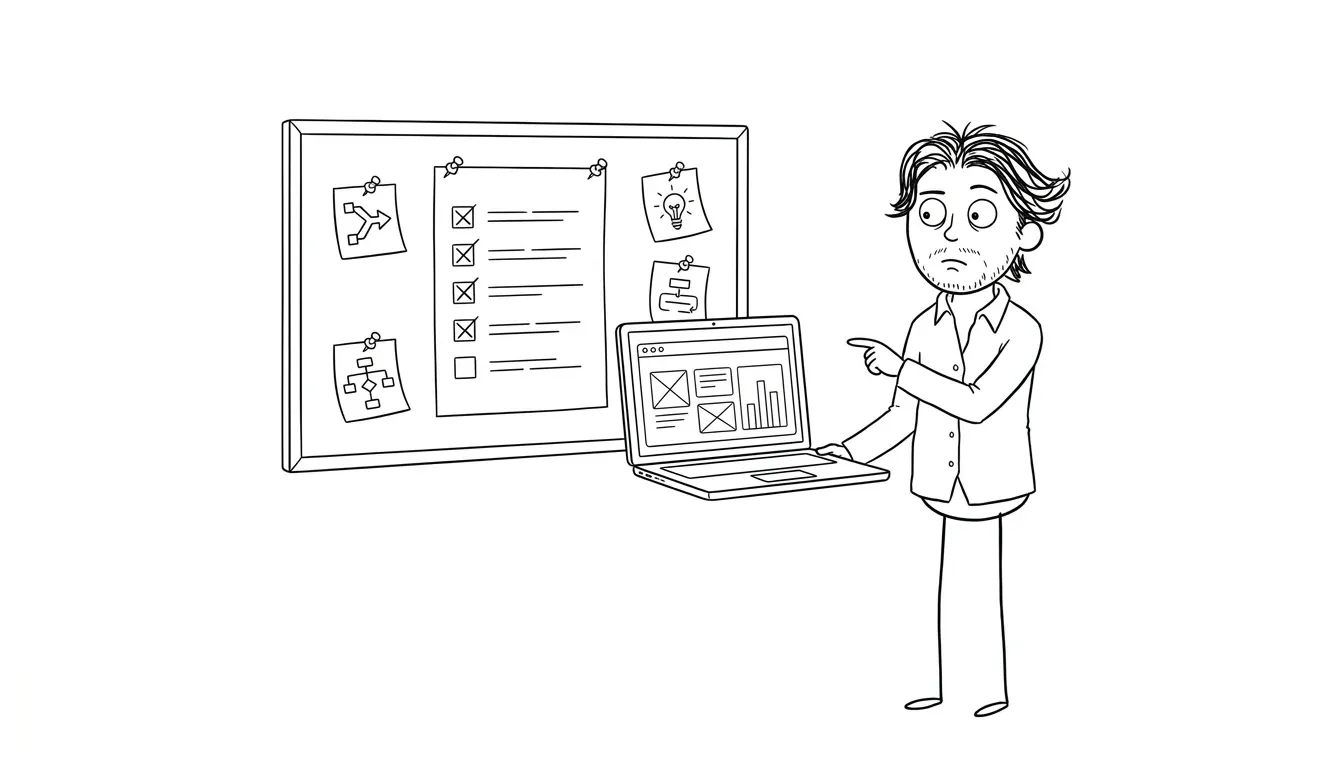
MVP permissions checklist: 9 launch-critical areas
1. Define the account boundary
The most important rule is often not a role. It is the boundary between one customer’s data and another’s.
Decide what owns each record:
- An individual account
- A workspace or organization
- A project within a workspace
- A parent account with multiple child accounts
- A system-owned record visible to selected users
Every protected request should derive access from that ownership relationship. Do not rely on a hidden button, a filtered list, or a record identifier that appears difficult to guess. A user who changes a URL or sends a direct API request should still be denied access to another account’s resource.
Write one acceptance criterion for every important boundary. For example:
Given a member of Workspace A, when that member requests a Workspace B project, the server denies the request without returning the project’s private fields.
2. Keep the first role model small
Use the fewest roles that represent real differences in responsibility. A collaborative MVP may only need:
- Owner: controls membership, billing, and destructive workspace actions
- Member: performs the core product workflow within the workspace
- Internal support: uses a separate, restricted operational path
Add another role only when it changes a launch-critical permission. If “editor” and “manager” behave identically in the first release, one role is enough for now.
Document what happens when a workspace has no available owner, whether ownership can transfer, and whether an account can belong to multiple workspaces. These edge cases shape the data model even if the settings interface stays simple.
Avoid a free-form permission builder in the first version. It multiplies combinations to design, implement, explain, and test. Fixed roles are usually easier to verify while the team learns which distinctions users actually need.
3. Enforce authorization on the server
Hiding a control in the interface improves clarity, but it is not a security boundary. Every protected read and write needs an authorization check where the server processes the request.
Verify that the same rule applies to:
- Page routes
- API endpoints
- Server actions
- File downloads
- Exports
- Background jobs triggered by a user
- Webhooks or integration callbacks that mutate account state
- Administrative tools
Centralize repeated rules where practical so different endpoints do not silently interpret the same role differently. The OWASP Authorization Cheat Sheet recommends least privilege, deny-by-default behavior, and validating permissions on every request. NIST defines least privilege as limiting access to the minimum needed for assigned tasks, which is a useful test for each MVP role.
A denied request should return a consistent response and avoid revealing unnecessary details. Logging should retain enough context to investigate the attempt without copying secrets or sensitive content into an unrestricted log.
4. Protect sensitive and destructive actions
Some actions deserve stronger controls than ordinary editing even when the same role performs them. Examples include:
- Deleting a workspace or account
- Transferring ownership
- Changing a billing owner
- Exporting a complete dataset
- Disconnecting an integration
- Revoking every active session
- Publishing content
- Changing another user’s role
For each action, define the required role, current state, confirmation, evidence, and recovery path. A destructive button should describe the actual consequence rather than using a generic “Are you sure?” prompt.
Consider reauthentication for especially sensitive actions when the product risk warrants it. At minimum, prevent stale pages and duplicate submissions from bypassing current authorization or repeating the operation.
5. Design invitations and membership changes
Invitations create temporary authority and need their own lifecycle. Decide:
- Who can invite someone
- Which roles can be assigned
- How long an invitation remains valid
- Whether an invitation can be revoked
- What happens when the email already belongs to an account
- Whether the invite is tied to a specific workspace
- How duplicate or forwarded invitation links behave
The acceptance flow should confirm the intended workspace and role before joining. Invitation tokens should be difficult to guess, limited in purpose, and invalid after use, expiry, or revocation.
Role changes also need explicit behavior. If an owner demotes a member while that member has an active session, determine when the new permissions take effect. Authorization should use current server-side state rather than trusting role information cached indefinitely in the browser.
6. Separate support access from customer roles
Internal support should not quietly use customer-owner permissions. Create a separate operational role or restricted tool with only the visibility and actions support genuinely needs.
Useful safeguards include:
- Individual staff accounts rather than shared credentials
- A reason or ticket reference before sensitive access
- Masked personal and payment data
- Read-only access by default
- Narrow, named support actions instead of arbitrary editing
- Audit events for access and state changes
- Prompt revocation during offboarding
If impersonation is essential, make the mode unmistakable, time-bound, and logged. Prevent sensitive actions unless specifically approved. Often a diagnostic view plus a few safe support commands is enough, especially when paired with the launch operations in the MVP admin dashboard checklist.
7. Record important permission changes
Current state cannot explain how access changed. Record append-only events for important administrative actions, including:
- Invitation created, accepted, expired, or revoked
- Member added or removed
- Role changed
- Ownership transferred
- Sensitive export requested
- Integration connected or disconnected
- Destructive action approved or completed
- Support access used
A useful event identifies the actor, target, action, time, outcome, and relevant reason. Avoid storing passwords, tokens, complete private payloads, or unnecessary personal data in the event text.
Audit history does not need a complex analytics interface. A protected list or searchable operational record may be enough for the MVP. The requirement is that launch-critical changes can be understood and traced.
8. Define offboarding and revocation
Removing a person should remove their effective access, not merely hide them from a member list.
Test what happens to:
- Active sessions
- API keys or personal tokens
- Pending invitations
- Integration credentials
- Owned records
- Assigned tasks or approvals
- Scheduled exports
- Shared links
- Workspace ownership
Decide whether records remain with the workspace, transfer to another owner, or become unavailable until reassigned. Prevent removal of the only owner unless a replacement is selected or the workspace is intentionally closed.
For internal staff, use the same discipline across the product, deployment platform, database tools, analytics, support systems, and third-party providers. Product permissions are only one part of operational access.
9. Test both allowed and denied behavior
Permission testing must cover more than successful interface clicks. For every role and protected action, test:
- The permitted role can complete the action.
- A lower-privilege role receives a denial.
- A signed-out request receives the correct response.
- A user from another workspace cannot access the resource.
- A direct URL or API request cannot bypass the interface.
- A stale session reflects a role removal or change.
- A revoked invitation cannot be reused.
- A destructive action checks the current state before executing.
- A denial does not leak sensitive fields.
- Important allowed and rejected actions create the expected evidence.
Write these as MVP acceptance criteria. Include the actor, starting state, request, expected response, and retained evidence. Automated tests are valuable for the stable policy rules; manual review should still verify the visible states and support workflow.
What can wait until after the MVP?
Defer access features that solve hypothetical scale rather than a current launch requirement. Candidates often include:
- Custom role builders
- Field-level permission editors
- Department hierarchies
- Bulk role administration
- Enterprise identity-provider integrations
- Formal approval chains for every action
- Complex temporary-access workflows
- Customer-facing audit analytics
Deferral does not mean leaving behavior undefined. State the first-release limit plainly. For example, the MVP may support one owner and members but not custom roles. Clear constraints are safer than interfaces that imply unsupported flexibility.
Some products do need stronger controls immediately because the product test involves sensitive information, regulated workflows, or multiple independent organizations. In that case, reduce feature breadth rather than weakening a required boundary. Legal or compliance requirements should be reviewed by qualified specialists; a checklist is not a certification.
Turn the checklist into a build-ready permission spec
Create one short specification with four parts:
- Resource map: every protected resource and its owner
- Role matrix: allowed and denied actions for each launch role
- Sensitive-action rules: confirmation, evidence, and recovery requirements
- Test cases: happy paths, denials, cross-account attempts, and revocation
Mark each row as a launch blocker, required soon, later improvement, or out of scope. Then connect every launch blocker to an owner and an acceptance criterion. This produces a focused build slice instead of a vague requirement to “add permissions.”
For a product with an unclear account model or risky workflow, a $500 Audit + Spec can examine one focused lens and turn the findings into a scoped decision. The fee is credited 100% toward follow-on work booked within 30 days.
When the core workflow, account model, and launch safeguards need to be designed and built together, Dee Agency’s $9,000 Idea to MVP service covers the focused path from concept to a working first release. Review the service overview, then share the product and its core account boundary to define the next step.
Got a project worth shipping? Send the brief.
Quote and kickoff date back in a day, usually faster. If it's not a good fit I'll say so.